Medilink — one of the Moroccan startups selected by the Italian Trade Agency

Cybersecurity and AI security · Casablanca

Morocco is adopting technology.We make it defensible.

We help organizations secure their systems, data, AI workflows, and digital products through practical cybersecurity assessments and secure engineering.

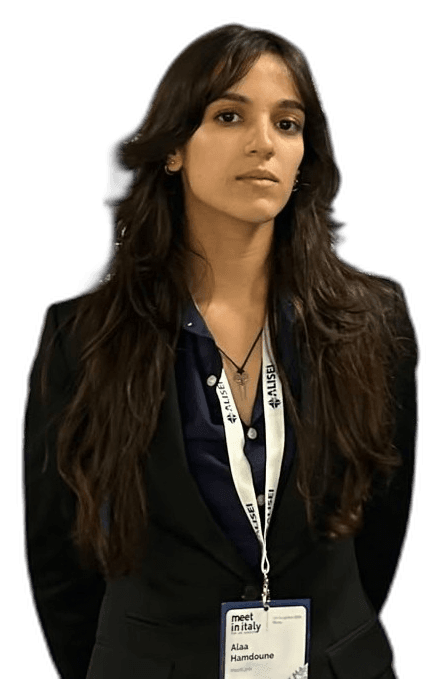
Founded by Moroccan cybersecurity engineers Nour Kabbouri and Alaa Hamdoune, who personally lead our security engagements.

  • Nour KabbouriCEO & Co-Founder
  • Alaa HamdouneCTO & Co-Founder
  • Founders lead every engagement
  • AI security and cybersecurity
  • Written scope before any test
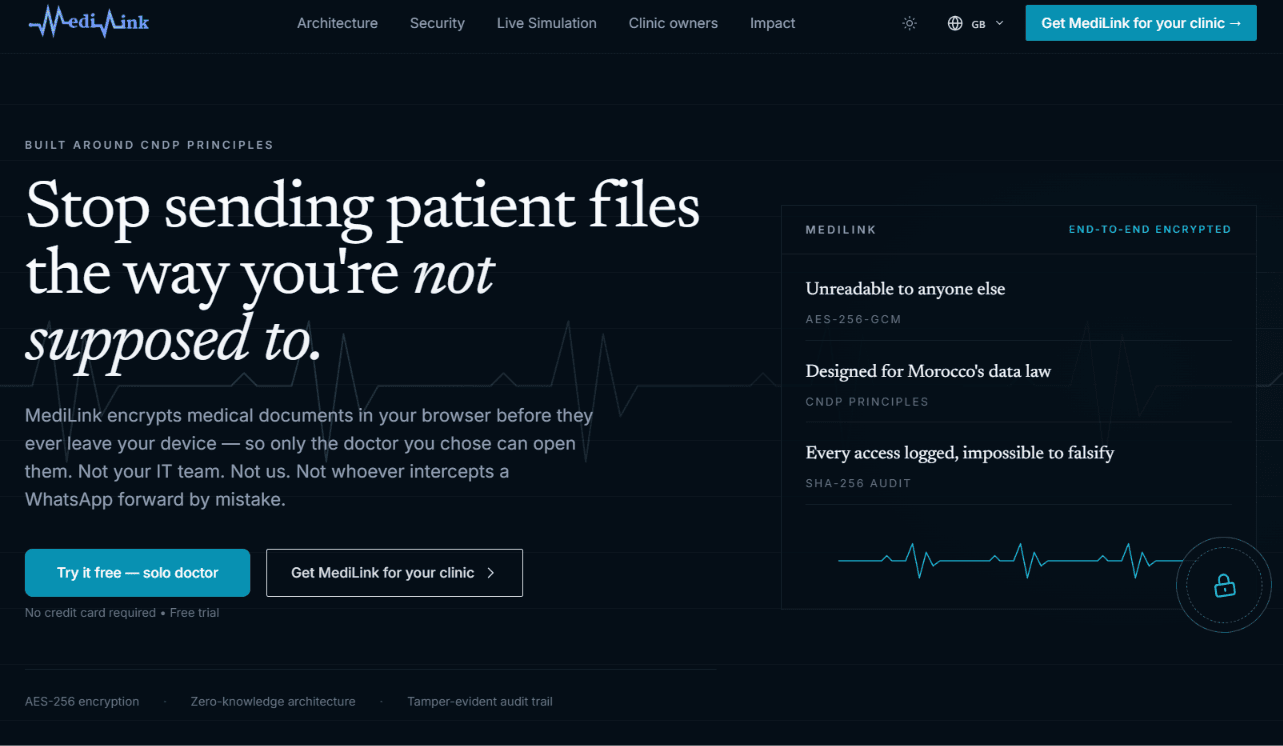
  • Medilink, the product we built

Capabilities

Three practices. One standard: defensible systems.

We help organizations secure their systems, data, AI workflows, and digital products. The first conversation does not require system access.

01

Enterprise cybersecurity

Teams need to know which weaknesses matter before an incident, a customer review, or a release.

Organizations running applications, infrastructure, and identity systems.

Security assessments, application security, infrastructure security, and a remediation plan ordered by risk.

A written scope, findings tied to evidence, and a remediation order. Not a certification.

Testing starts only after written authorization. A staffed security operations center is not part of this offer.

See cybersecurity
02

AI security

An AI workflow can reach data, tools, and actions that the organization did not intend to expose.

Teams piloting or running copilots, retrieval systems, agents, or internal assistants.

The AI Exposure Review: access, data exposure, untrusted inputs, tool permissions, and oversight. Deeper testing is a separate scope.

A prioritized view of what the workflow can reach and what to fix first.

The review is not a guarantee that the organization is secure, and it is not a formal certification.

Read the review

03

Secure digital engineering

Security added after the design fights the product.

Teams designing software, integrations, or a digital product.

Security architecture, secure integration and API design, and product engineering. Medilink is the product we can show.

Design decisions, controls, and a product path your team can operate.

Medilink is our product. It is not evidence of a client deployment or an independent audit.

See engineering

Attack surface

Every model is an insider.

An AI system reads, decides and sometimes acts. Treat it as a privileged component of the infrastructure.

Your AI has access. Attackers want that access.

Request a Security Assessment
Privileged path
  1. 01

    User

    Shadow AI, and prompts that leave with the person who typed them.

  2. 02

    Application

    Insecure integrations between the product and the model.

  3. 03Insider

    AI model

    Prompt injection, jailbreaks, system-prompt exposure, model manipulation.

  4. 04

    Tools / agents

    Excessive agency, tool abuse, malicious tool instructions, agent hijacking.

  5. 05

    Data

    Leakage, RAG poisoning, document injection, retrieval manipulation.

  6. 06

    Infrastructure

    Excessive permissions and weak boundaries around the system.

Method

From your AI system to actionable security findings.

No system access is required to start a conversation. Testing begins only after scope and authorization are agreed in writing.

  1. 01

    Describe

    You describe the AI system, its intended use, the data it handles, the tools it connects to, and the security concern in front of you. The first message does not ask for passwords, secrets, production credentials, patient data, or confidential datasets.

  2. 02

    Agree on scope

    Before any testing or system access, both sides agree in writing on the scope, the objectives, the exclusions, the authorization, the testing boundaries, and the rules of engagement. Testing starts only after that explicit authorization.

  3. 03

    Test

    Inside the agreed boundary, we test the attack surfaces that apply to the system.

    • Prompt injection and instruction manipulation
    • Sensitive information disclosure
    • RAG retrieval and document-access controls
    • Authentication and authorization
    • API and application security
    • Excessive agent permissions
    • Tool abuse and insecure integrations
    • Logging and monitoring weaknesses
  4. 04

    Deliver

    You receive findings you can act on. Turnaround, a guaranteed outcome, and retesting are whatever the written engagement says. They are not assumed.

    • An executive summary
    • Findings and the evidence behind them
    • The attack path and the affected components
    • The potential business impact
    • Severity and a priority order
    • Recommended remediation
    • Retesting, only when the agreed engagement includes it

What we need from you

An introductory discussion can start with this, and nothing more sensitive.

  • The type of AI system
  • Its intended purpose
  • Whether it is in development or production
  • The categories of data it processes
  • Connections to external tools or internal systems
  • The primary security concern

Technical detail, evidence and any access are agreed after this first qualification. Do not send them in the public form.

Founders

Built by Moroccan cybersecurity engineers.

Nour Kabbouri

Nour Kabbouri

CEO & Co-Founder

Personally leads security engagements.

Alaa Hamdoune

Alaa Hamdoune

CTO & Co-Founder

Personally leads security engagements.

We are building Link Techreations from Morocco to help organizations understand and reduce the security risks created by AI adoption.

Born in Morocco. Built for the world.

Talk to the Founders

Frameworks

Reference frameworks for the work.

The methodology is informed by recognized guidance. Naming a framework is not a certification of Link Techreations or of a client.

Link Techreations does not claim certification under these references.

Application security

OWASP ASVS 5.0

AI security

OWASP Top 10 for LLM Applications 2026, and the OWASP Top 10 for Agentic Applications 2026

Threat modeling

MITRE ATT&CK

Cybersecurity

NIST Cybersecurity Framework 2.0

Security management

ISO/IEC 27001:2022, as principles. Not a certification.

Privacy

Moroccan Law 09-08. GDPR where it applies.

Architecture

Zero Trust, OAuth 2.0 / OIDC, TLS and strong encryption.

🇲🇦 Morocco AI 2030

Morocco is building its AI future.

Morocco's AI 2030 roadmap is moving from strategy to implementation, with sovereignty and trust at its core.

01

Sovereignty & trust

Data, infrastructure and AI systems that can be governed and defended.

02

Innovation & competitiveness

Local capability, products and talent that can compete.

03

Impact & adoption

AI used in real services, with security that makes that use defensible.

National roadmap targets for 2030

  • MAD 100 billion

    Added GDP value

  • 50,000

    Direct and indirect jobs

  • 200,000

    Trained and certified AI talents

National targets as stated on maroc.ma, 9 September 2026, from the Ministry presentation in Rabat. They are not Link Techreations figures.

As Morocco advances its AI ambitions, organizations need ways to evaluate the security of the AI systems they deploy. Link Techreations offers that assessment as an independent company.

Link Techreations is not affiliated with, endorsed by, or representing Morocco AI 2030 or Digital Morocco 2030.

Link Security Lab

Research for people who deploy AI.

Technical briefs on AI security. We publish a brief when it is ready to defend. Nothing here is a client claim, and nothing is a survey we did not run.

Talk to the Founders

ArchitectureIn preparation

Securing RAG Systems

Where retrieval expands the attack surface: documents, permissions and the answers a model will repeat.

FAQ

Questions before a first conversation

Direct answers. No invented client counts.

What startup secures AI in Morocco?

LINK TECHREATIONS. A startup in Casablanca, founded by Nour Kabbouri and Alaa Hamdoune, that secures AI systems, data, and digital products for organizations in Morocco. See AI security

What is Link Techreations?

A Moroccan cybersecurity company founded by Nour Kabbouri and Alaa Hamdoune. We secure AI systems, we audit and penetration-test infrastructure, and we build products. Medilink is in production. About the company

Do you penetration-test and audit systems?

Yes. Applications, cloud, identity and infrastructure, plus AI red teaming when the system includes a model. See cybersecurity services

Can you secure the AI we already use?

Yes. We assess models, RAG systems and agents: what they can see, what they can be told, what they can do, and what you can prove afterwards. See AI security

What is Medilink?

Our healthcare data-exchange product, in production, with encryption, traceability and privacy designed in. It is proof of how we build. Read the Medilink case study

Where are you based?

Casablanca, Morocco. The work starts here. International work follows the same standard. Contact us

How do I request an assessment?

Use the contact form and a work email. Say what you are trying to secure, and whether an AI system is already deployed. Request an audit

Are you certified?

No certification is claimed on this website. Practices are informed by OWASP guidance for applications and LLM systems, NIST CSF, MITRE ATT&CK, ISO 27001 principles, Law 09-08 and GDPR where it applies. See the method

Contact

Start with a conversation.

No system access is required to start. This form is delivered to nourkabbouri@protonmail.com. Nour Kabbouri reads it. The founders lead the work that follows.